FREE LIVE WEBINAR
FOR SOC EXPERTS

See how AI investigates your alerts, live

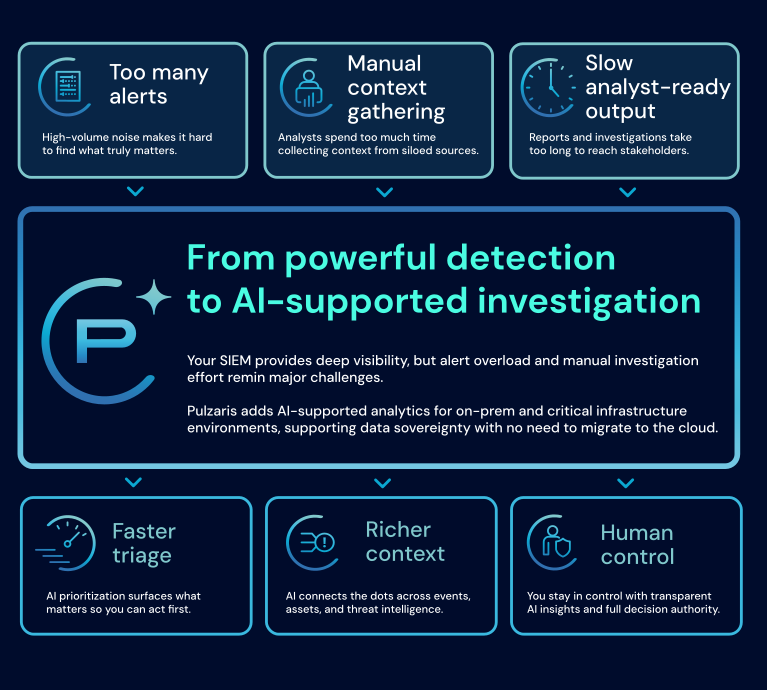
Join our webinar to see how PULZARIS Analyst Agent turns alerts into analyst-ready decisions faster, while your analysts stay in control. 

Real-world MSSP experience · Practical insights · Live demo 
27 November 2026 · 10:00–11:00 CET · Online 

60 minutes · English · Microsoft Teams 

Register for the free webinar

Free to attend. Includes a live demo and Q&A. 

What you’ll see in this webinar:

Discover how AI-assisted investigation works in real SOC operations — beyond product promises. 

  • Live demo: See how PULZARIS Analyst Agent turns SIEM alerts into analyst-ready investigation briefs. 
  • Real-world results: Learn from MSSP experience, including insights from 3,000+ investigated incidents. 
  • Practical workflow: Explore AI-supported triage, enrichment, correlation and human validation. 
  • Deployment & data protection: Understand how controlled, on-prem deployment supports sensitive SOC environments.


Learn from real-world experience with AI-assisted incident investigation in live customer environments. 

27. November 2026. CET 10:00-11:00
Beyond Detection: The Investigation Challenge

Too many alerts, fragmented context and manual investigation slow SOC teams down. Discover how AI-assisted investigation helps address these challenges while keeping analysts in control. 
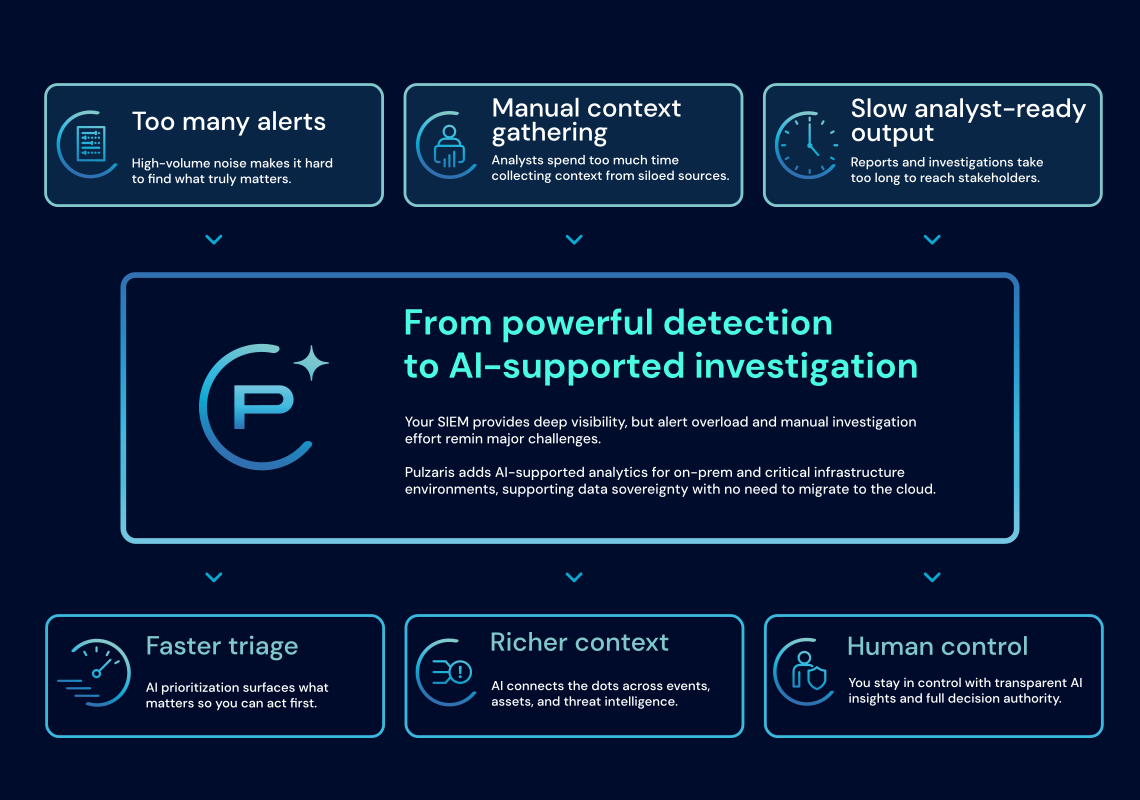
Your SIEM remains the detection foundation.
PULZARIS is an on-prem investigation layer powered by AI.

PULZARIS does not replace the SIEM. It adds AI-powered triage, enrichment, prioritization and investigation support on top of your existing SOC workflow.

SIEM

PULZARIS Analyst Agent

Incident Intelligence Brief
SOC human Analyst

AI-powered investigation capabilities for SOCs

Alert Triage

Start with a validated SIEM foundation and AI-supported investigation from the beginning.

Prioritize alerts and highlight what matters most.

Contextual Investigation
Build context across logs, endpoints, network, indentity and events.
Entity Mapping
Link users, IPs and assets to reveal relationships and blast radius.
Threat Enrichment
Add reputation data, IOCs and threat intelligence for deeper context.
Risk & Confidence
Score incidents with risk and confidence to guide analyst prioritization.
Analyst-ready Briefs
Generate structured summaries with evidence, verdict and recommended action.
Leverage existing on-prem infrastructure
Deploy PULZARIS in a controlled environment close to sensitive SOC data.
Built around real SOC workflows

Developed and validated through real-world SOC investigation workflows.

Help control AI operating costs
Reduce cloud processing and keep AI operating costs predictable.
From SIEM alert to analyst-ready decision
Trust by Design. Security by Default.
Data sovereignty support

Helps keep sensitive SOC telemetry under customer control.

Data obfuscation & encryption

Sensitive data can be masked, replaced and protected with encryption.

Controlled deployment

Supports customer-controlled and on-prem deployment models.

Evidence-backed outputs

Shows evidence, confidence and reasoning for analyst validation.

WHY PULZARIS

Built on real SOC and experience

PULZARIS was shaped by hands-on SOC operations, SIEM expertise and real-world investigation workflows.

20+

years of SOC experience

55

experts

3000

investigated incidents

FAQ
Is PULZARIS a replacement for my SIEM?

No. PULZARIS does not replace your SIEM. It adds an AI-powered investigation layer to existing SOC workflows, helping analysts move faster from alert to context, verdict and recommended action.

PULZARIS Analyst Agent was initially developed and validated with NetWitness SIEM. Its architecture is designed to support broader SIEM integrations, depending on available APIs, telemetry quality and customer-specific requirements.

No. PULZARIS supports the investigation process with context, enrichment, scoring and recommended actions, but human analysts remain responsible for validation, escalation and final operational decisions.
PULZARIS is designed for controlled enterprise SOC environments. Sensitive data can be masked, replaced and protected with encryption, while customer-controlled or on-prem deployment models help keep SOC telemetry under control.

PULZARIS is designed for enterprise SOC teams, MSSPs, MDR providers and organizations that want to reduce repetitive investigation work while keeping analysts in control. 

Thank You for Your Interest

Your request has been successfully submitted. You can now access the document below.

We’re glad you registered for our webinar.
We’ll be in touch shortly via email with the details.

Unlock Exclusive Insights

Be among the first to access premium PULZARIS content. Complete the form below and download the document instantly.

jQuery(document).on('submit_success', function(event, response){ dataLayer.push({ event: 'elementor_form_success', form_name: response.data.settings.form_name }); });
Privacy Overview

This website uses cookies so that we can provide you with the best user experience possible. Cookie information is stored in your browser and performs functions such as recognising you when you return to our website and helping our team to understand which sections of the website you find most interesting and useful.